Understanding OAuth: Simplifying Secure Authorization
OAuth (Open Authorization) is a protocol that allows secure, third-party access to user data without sharing login credentials. It uses access tokens to grant limited, time-bound permissions to applications.
By Ayushmaan Dwivedi · · 3 min read
Authentication and authorization are core to building secure and user-friendly applications. In this blog, we’ll delve deep into OAuth’s conceptual framework, its practical applications, and the technical details.
What is OAuth?
OAuth stands for Open Authorization. It’s a protocol that allows third-party applications to request limited access to a user's resources without exposing their credentials. For example, when you log into a website using your Google account, OAuth handles the flow, ensuring that Google verifies you and shares only the required information with the requesting website.
Authentication vs. Authorization
While these terms are often used interchangeably, they are distinct:
Authentication: Confirms the user’s identity (e.g., "Who are you?").
Authorization: Determines the user’s access rights (e.g., "What are you allowed to do?").
OAuth bridges these two concepts by allowing applications to authenticate users indirectly through an authorization mechanism.
The Problem OAuth Solves
Traditional username-password systems create several challenges:
Password Overload: Users must remember dozens of passwords.
Security Risks: Reusing passwords or storing them insecurely leads to vulnerabilities.
Friction in Onboarding: Startups often struggle with user signups due to the hesitance of creating yet another account.
OAuth mitigates these issues by leveraging existing accounts from trusted platforms like Google, Meta, or GitHub etc. Users can authenticate and authorize applications with just a few clicks.
How OAuth Works
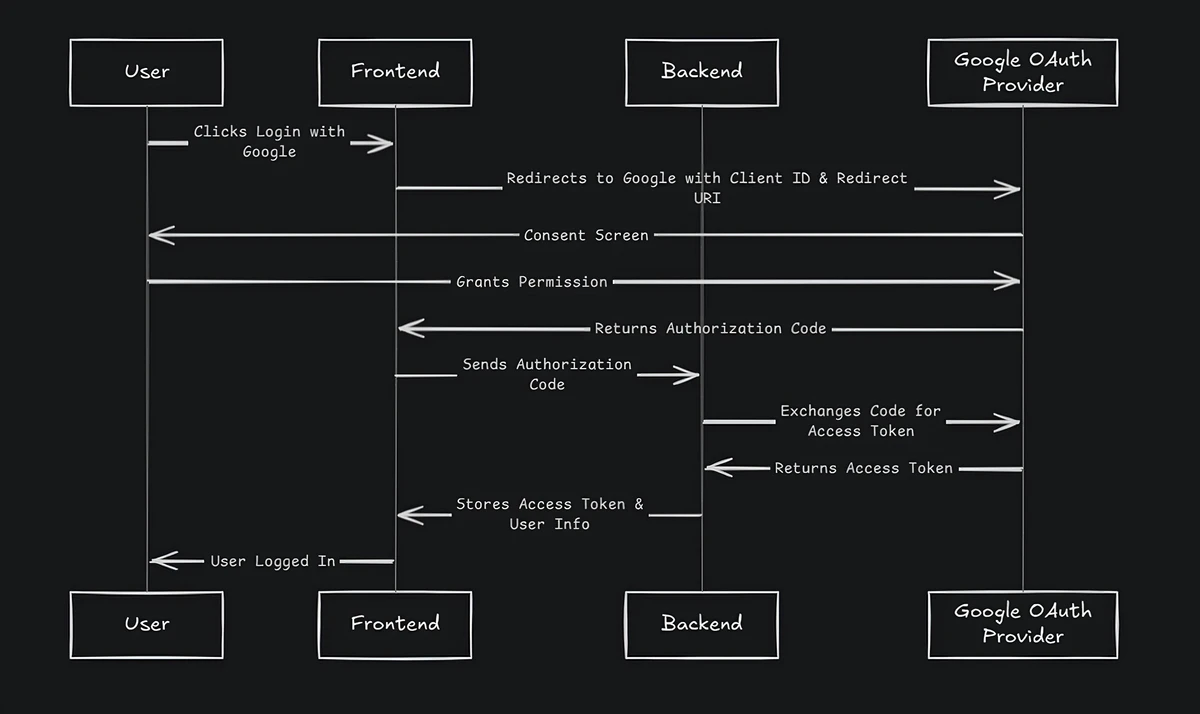
Let’s break down the OAuth flow step by step, and understand how the frontend, backend, and OAuth provider interact:
User Requests Access: The user visits a third-party website (e.g., a startup) and opts to sign up or log in using an OAuth provider (e.g., Google).
Authorization Request: The third-party website redirects the user to Google’s OAuth server, requesting specific permissions, such as access to the user’s name and email.
User Consent: Google presents a consent screen, outlining what information will be shared. The user approves or denies the request.
Authorization Grant: Upon approval, Google provides an authorization code to the frontend application.
Access Token Exchange: The frontend sends the authorization code to the backend server, which exchanges it for an access token by making a secure request to Google’s OAuth server.
Data Access: The backend uses the access token to retrieve the necessary information (e.g., the user’s name and email) and stores the token securely.
Session Management: The backend logs the user in and provides a session token to the frontend for subsequent user actions.
Benefits of OAuth
Enhanced User Experience:
Simplified signups with just a few clicks.
No need to remember multiple passwords.
Offloaded User Verification:
The burden of verifying user identity shifts to trusted providers like Google or Facebook.
Standardization:
OAuth’s standardized flow makes implementations predictable and secure.
Increased Signups:
Case studies, such as the Interview Ready example, show how OAuth integration can double or triple signups by reducing friction.
Mobile-Friendly:
Especially useful on mobile devices where typing usernames and passwords is cumbersome.
Practical Implementation
Here’s a simplified implementation using OAuth 2.0 with Google:
Step 1: Register Your Application
Sign up in Google’s Developer Console and create a new project. Enable the OAuth 2.0 APIs and configure a redirect URI for your application.
Step 2: Authorization URL
Redirect users to Google’s authorization URL:
const clientId = "YOUR_CLIENT_ID"; const redirectUri = "YOUR_REDIRECT_URI"; const scope = "profile email"; const authUrl = `https://accounts.google.com/o/oauth2/auth? client_id=${clientId}& redirect_uri=${redirectUri}& scope=${scope}& response_type=code`; window.location.href = authUrl;Step 3: Handle the Callback
When the user is redirected back, extract the authorization code from the URL.
const urlParams = new URLSearchParams(window.location.search); const authorizationCode = urlParams.get("code");Step 4: Exchange Code for Access Token
Send a request to Google’s token endpoint:
const tokenResponse = await fetch("https://oauth2.googleapis.com/token", { method: "POST", headers: { "Content-Type": "application/x-www-form-urlencoded", }, body: new URLSearchParams({ code: authorizationCode, client_id: "YOUR_CLIENT_ID", client_secret: "YOUR_CLIENT_SECRET", redirect_uri: "YOUR_REDIRECT_URI", grant_type: "authorization_code", }), }); const tokenData = await tokenResponse.json(); const accessToken = tokenData.access_token;Step 5: Fetch User Info
Use the access token to fetch user details:
const userInfoResponse = await fetch("https://www.googleapis.com/oauth2/v2/userinfo", { headers: { Authorization: `Bearer ${accessToken}`, }, }); const userInfo = await userInfoResponse.json(); console.log(userInfo);
Conclusion
OAuth transforms how we handle authentication and authorization. By offloading verification to trusted providers, we streamline user onboarding, reduce security risks, and enhance application scalability. However, thoughtful implementation and understanding of its limitations are essential to maximize its benefits.
If you’re a startup or enterprise looking to improve user experience and security, integrating OAuth could be a game-changer.